
Too often, we focus on securing small businesses or enterprise environments, and completely ignore (or forget!) the home users. From grandma, who browses the internet and thinks that clicking on every ad is a great idea, to your employee with a personal device - This blog post explores key ideas to protect home users at all levels.
Security hardening is always a balance between security and usability. Some of the recommendations in this article can affect application compatibility. Make changes gradually, understand what a setting does, and make sure important files are backed up before making significant configuration changes.
Windows Security
Before installing additional security software, take a look at something which already comes with your computer - Microsoft Security. This is often overlooked but provides some very real benefits for your average home user.
Windows Security is Microsoft's built-in security interface and brings together several important protections, including:
- Microsoft Defender Antivirus
- Windows Firewall
- App & browser control
- Device security
- Account protection
- Exploit protection
Microsoft Defender Antivirus provides real-time malware protection and is included with Windows 11.
This shouldn't be confused with the separate Microsoft Defender application included with Microsoft 365 Personal and Family subscriptions. Microsoft Defender Antivirus is built into Windows at no additional cost, whereas the Microsoft Defender app adds security capabilities across supported Windows, macOS, Android and iOS devices for Microsoft 365 subscribers.
Microsoft documentation: Stay protected with Windows Security
Check Defender is actually protecting you.
Open: Windows Security → Virus & threat protection
Check that:
- Real-time protection is enabled
- Cloud-delivered protection is enabled
- Automatic sample submission is enabled
- Tamper Protection is enabled
You should also make sure security intelligence updates are being installed. Microsoft Defender Antivirus receives continually updated threat intelligence, allowing Microsoft to identify malicious files and behaviours as threats evolve.
Installing another antivirus product may cause Microsoft Defender Antivirus to move into a different operating mode, so don't simply stack multiple antivirus products together in the belief that more antivirus automatically means more protection, oftentimes this actually has an adverse effect!
Keep Windows Updated
One of the simplest security improvements you can make is also one of the most important: Install updates.
Attackers routinely take advantage of vulnerabilities for which security updates already exist.
Open: Settings → Windows Update
Make sure Windows Update is enabled and regularly check for outstanding updates.
For most home users, I would strongly recommend allowing Windows to automatically download and install security updates rather than delaying them indefinitely.
But Windows itself isn't the only thing that needs patching. Don't forget your applications!
Application Patching
Your browser, PDF reader, compression utilities, communication software and other applications can all contain vulnerabilities. The problem is that Windows Update doesn't necessarily maintain every third-party application installed on your computer.
Fortunately, there are some excellent options for automating this.
(Note that the below isn't an exhaustive list. Other options exist, and those listed below are in no particular order.)
Option 1: Winget Autoupdate
Windows Package Manager, or Winget, provides a package-management system for Windows Applications. You can see a list of available updates with:
winget upgrade
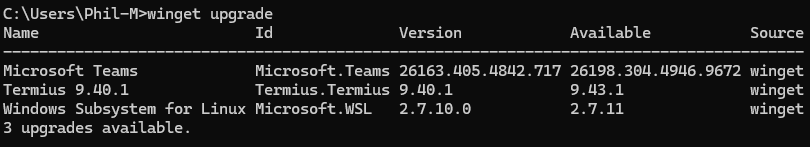
We can update all of these applications using the command:
winget upgrade --all
However rather than remember to periodically run this command, we can automate the process.
The community-developed Winget-AutoUpdate (WAU) project by Romanitho uses WinGet to automatically check for and update supported applications on a scheduled basis.
Installation can even be performed through WinGet:
winget install Romanitho.Winget-AutoUpdateWAU supports features such as application blocklists and allowlists and can automatically maintain itself.
Option 2: Patch My PC Home Updater
Sometimes for home users, it's easier to "set and forget" - This is made very possible thanks to a tool such as Patch My PC Home Updater. (Other tools exist). If you'd prefer something more graphical, this is the tool for you!
The Home Updater is free for personal use and can install and update hundreds of commonly used Windows applications. That makes it particularly useful for friends or family members who aren't necessarily going to open PowerShell and run WinGet commands every week.
Whichever solution you choose, the important part is establishing a process where applications aren't forgotten simply because Windows itself is patched.
Hint: For those of us who are the family IT Service Desk, Home Updater provide a portable EXE - Throw this on a USB stick to save your sanity! 😄
Turn on reputation-based protection
Located under Windows Security → App & browser control → Reputation-based protection. Microsoft Defender SmartScreen helps protect against malicious websites, phishing pages, suspicious applications and potentially malicious downloads.
Microsoft uses signals including website, file and publisher reputation to determine whether something might be dangerous. For most home users, I recommend leaving the available SmartScreen and potentially unwanted application protections enabled.
These controls provide an important layer between: "I've downloaded something" and: "Windows has executed it." - That distinction matters. It could very easily be the difference between "Oh shit." and "That was close, but Windows protected me."
Enable Attack Surface Reduction (ASR) rules
This one is often overlooked for home users. Importantly, ASR rules aren't exclusively an enterprise Microsoft Defender for Endpoint feature. Microsoft documents that ASR rules are a Microsoft Defender Antivirus capability available on Windows editions that include Defender Antivirus - including Windows 11 Home.
Microsoft Defender Attack Surface Reduction (ASR) rules restrict behaviours frequently abused by attackers.
ASR rules can restrict behaviours including:
- Credential theft from LSASS
- Malicious or suspicious scripts
- Executables launched from email or webmail
- Office applications creating child processes
- Office applications injecting code into other processes
- Executables launched from USB storage
- Abuse of vulnerable signed drivers
- WMI-based persistence
Microsoft maintains a complete reference here: Attack Surface Reduction rules reference
However, DO NOT blindly enable everything. (Seriously, otherwise you'll be getting a lot of phonecalls when things don't work...) ASR rules can break legitimate applications.
Where possible, start potentially disruptive rules in Audit or Warn mode before changing them to Block. The goal isn't to switch every security control to its most aggressive setting.
Protect Windows Credentials With Device Guard and Credential Guard
Modern Windows devices can use virtualization-based security (VBS) to isolate particularly sensitive components of Windows from the normal operating system. One of the most useful capabilities is Windows Defender Credential Guard.
Credential Guard uses virtualization-based security to isolate secrets such as NTLM password hashes and Kerberos credentials from the main operating system, This makes traditional credential-dumping techniques significantly more difficult. For a home user, this could seriously protect their digital identity.
On supported Windows 11 devices, many of these protections may already be enabled, but it is always worth checking.
Open: Windows Security → Device security → Core isolation and review the security capabilities available on your computer. Where supported, I recommend enabling Memory integrity.
Hardware support and Windows edition can affect the functionality available, so check Microsoft's current documentation before manually enforcing Device Guard or Credential Guard policies.
UAC - Don't disable it just because...!
I get it, sometimes UAC prompts are annoying, and for home users it is easy to say "It's my laptop, I'm the admin, go away." But seriously, don't just disable it for the sake of it.
UAC limits applications running under a normal user token and requires elevation when an operation needs administrator privileges. That provides an important security boundary between everyday activity and administrative changes.
Microsoft's default configuration is appropriate for most people.
If you'd prefer a stricter configuration, search for: Change User Account Control settings and consider Always notify. The slight inconvenience of occasionally approving a legitimate administrative operation is significantly preferable to allowing every process to silently execute with elevated privileges.
Consider a standard user account
Controversial, I know. But does your nan really need an administrative account as her daily user...?
Consider using a standard Windows account for everyday activity and maintaining a separate administrator account exclusively for administrative changes. That means web browsing, email, documents and normal applications operate without administrative rights. (By the way, you should be doing this in a business environment - If you're not, please change it...!)
If administrator privileges are required, Windows can request credentials for the administrator account.
Windows Firewall
Windows Firewall is another security control that people sometimes disable while troubleshooting and subsequently forget to turn back on. The Windows Firewall should be considered essential. Don't just disable it for the sake of it...
In Windows Security → Firewall & network protection, you should see firewall protection enabled for the applicable network profiles. Ensure that this is enabled. I would advise that the setting for public networks should be to block inbound connections by default.
For most home users, the default Windows Firewall configuration provides an excellent balance between security and usability.
Disable Autorun and AutoPlay
USB drives remain an easy way of moving data between computers, but they're also an attractive attack vector. Windows AutoRun historically allowed applications referenced by removable media to launch automatically. There's rarely a good reason for a modern home computer to automatically execute software simply because removable media has been inserted.
At minimum, disable AutoRun. Security-conscious users may also choose to disable AutoPlay completely. On supported versions, this can be managed through group policy but you may wish to use this script from Jay Kerai
Disable AutoRun
# Define the registry key and value name
$regPath= "HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer"
$key0 = "NoAutorun"

# Check if the value exists and is already set to 1
if ((Test-Path $regKey) -and (Get-ItemProperty $regKey -Name $key0 -ErrorAction SilentlyContinue).$key0 -eq 1) {
    Write-Host "The value of '$key0' is already set to 1."

}
else {
try {
    # Set the value
    Set-ItemProperty -Path $regKey -Name $key0 -Value 1 -Type DWORD -Force
    Write-Host "The value of '$key0' has been set to 1."
}

catch {
    Exit 0
}
}
Disable AutoPlay
# Define the registry key and value name
$regKey= "HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer"
$key0 = "NoDriveTypeAutoRun"

# Check if the value exists and is already set to 1
if ((Test-Path $regKey) -and (Get-ItemProperty $regKey -Name $key0 -ErrorAction SilentlyContinue).$key0 -eq 1) {
    Write-Host "The value of '$key0' under $regKey is already set to 1."

}
else {
try {
    # Set the value
    Set-ItemProperty -Path $regKey -Name $key0 -Value 1 -Type DWORD -Force
    Write-Host "The value of '$key0' under $regKey has been set to 1."
}

catch {
    Exit 0
}
}
Protect your DNS
Endpoint security only protects one part of the equation. What if we could stop your friends and family from even visiting a known malicious website?
Instead of simply using whichever DNS resolver your internet provider supplies, consider using a protective DNS service.
Protective DNS services can block requests to domains associated with:
- Malware
- Phishing
- Command-and-control infrastructure
- Cryptomining
- Newly observed malicious infrastructure
- Potentially unwanted content
Depending on the service, filtering may happen before your browser ever establishes a connection with the malicious website.
Options worth researching include services such as:
- Cloudflare
1.1.1.1 for Families - Quad9
- NextDNS
- Control D
For more technical users, services such as NextDNS and Control D can provide custom policies and logging, allowing you to create something approaching a lightweight security gateway for your home network.
For those who wish to try NextDNS, check out my blog post on this here:
 Philip Marsh
Protect your browser credentials
Browser credential theft remains an extremely lucrative target for attackers. Our browser has effectively become another operating system, for many people it contains access to email, banking, cloud storage, social media and numerous other services.
One interesting recent example involves credentials stored by Microsoft Edge. Security research demonstrated that saved Edge credentials could be extracted from browser process memory by a process with sufficient privileges.
Keeper has developed a capability called Keeper Forcefield, which uses a kernel-level driver to prevent unauthorised processes from accessing the memory of protected applications and browsers. According to Keeper, Forcefield protects applications including Edge, Chrome, Firefox, Brave, Opera and Vivaldi against this type of memory access.
You can read Keeper's technical explanation here:
How Keeper Forcefield protects against Microsoft Edge's password vulnerability
NOTE: Keeper Forcefield does not require an active Keeper subscription.
There are of course other options available, but the key point here remains simple: Don't treat a browser password vault as an impenetrable security boundary.
Use MFA.
That's it. That's the headline.
Hardening the computer is only part of protecting your digital life. Your online accounts matter too. Where available, you should use passkeys. For accounts that don't support passkeys, enable multi-factor authentication.
Ideally use:
- Passkeys or hardware-backed authentication
- Authenticator applications
- SMS only where stronger options aren't available
- It is worth noting that MFA on SMS is deemed inherently insecure and is susceptible to attacks such as SIM Swapping
Your Microsoft account in particular deserves strong protection because it may be connected to Windows, OneDrive, Outlook and other services.
Turn on Drive Encryption
What happens if somebody steals the entire computer?
Without disk encryption, an attacker may be able to remove the storage device or boot another operating system and access files, potentially without knowing your Windows password. Windows provides BitLocker Encryption capabilities depending on your hardware and Windows edition.
Search Settings for: Device encryption and check whether encryption is enabled.
Windows Pro users can also manage BitLocker through: Control Panel → BitLocker Drive Encryption
Make absolutely sure your BitLocker recovery key is securely backed up. The last thing you want is to be locked out of your own data...!
Speaking of... Back up your data.
Security isn't only about preventing someone from accessing your data. It's also about ensuring you can recover it.
Maintain backups of anything you can't afford to lose. For particularly important information, consider the 3-2-1 principle:
- 3 copies of your data
- 2 different types of storage
- 1 copy stored separately/off-site
This all sounds complicated, are there community tools that can help?
One of the things I love about the security community, is the amount of high-quality work people make publicly available for free. (Seriously - Some of you guys absolutely rock!)
There are two projects I'd specifically recommend security-conscious Windows users investigate (There are more, but I have tried both of these and can personally recommend them)
Harden Windows Security — Violet Hansen / HotCakeX
Violet Hansen (@HotCakeX) maintains the excellent open-source Harden Windows Security project, the project focuses on hardening Windows using security functionality provided and supported by Microsoft (Many of which we have covered in part above).
What I love about this project is that you can backup and restore your security profiles, so if you have a profile that you know just works then you can restore this on your family members' devices and quickly and easily secure them!
Project: HotCakeX/Harden-Windows-Security
Harden System Security guide: Harden System Security Wiki
Windows Hardening Scripts - Jay Kerai / JKerai1
Another useful community resource is WindowsHardeningScripts by jkerai1. This repository contains PowerShell and command-line examples covering a huge range of Windows hardening areas.
There is, however, an extremely important warning attached to this one. The project's own README warns:
"Some scripts may brick your environment, review carefully"
This one is aimed at the more professional users who understand what they are doing. Do not just blindly run these scripts. The scripts can be used as a starting point to quickly implement protections as needed.
Project: jkerai1/WindowsHardeningScripts
Frequently Asked Questions
Is Microsoft Defender Free?
Microsoft Defender Antivirus is built into Windows 10 and Windows 11 at no additional cost and is managed through Windows Security.
The separate Microsoft Defender app is included with Microsoft 365 Personal and Family subscriptions and provides additional protection and security management across supported devices.
Do I need another antivirus program with Microsoft Defender?
For many home users, Microsoft Defender Antivirus combined with Windows' other built-in security capabilities provides a strong security baseline.
Installing multiple real-time antivirus products can cause compatibility and performance issues and doesn't automatically provide better protection.
Should I enable every Attack Surface Reduction rule?
Most likely not.
Some ASR rules can interfere with legitimate applications or workflows. Understand each rule and, where possible, evaluate potentially disruptive rules using Audit or Warn mode before enforcing them.
Should I disable UAC?
No. UAC provides an important layer of protection against applications silently performing operations requiring administrator privileges.
Should I use a custom DNS provider?
A reputable protective DNS service can provide an additional layer of security by preventing your computer from resolving domains known to be associated with malicious activity.
Is Windows Firewall enough?
For most home users, Windows Firewall provides strong host-based firewall protection when correctly enabled. You generally don't need to install a separate firewall application simply because you're using Windows.
Philip Marsh
Writing practical notes on Microsoft security, identity protection, detections, and building safer systems.
View all posts